Removing names does not settle whether a file belongs in an AI prompt. Routes, timings and trip counts can still reveal how a business operates. Start with the person who understands that information.
Glenn's example: the value is in the pattern
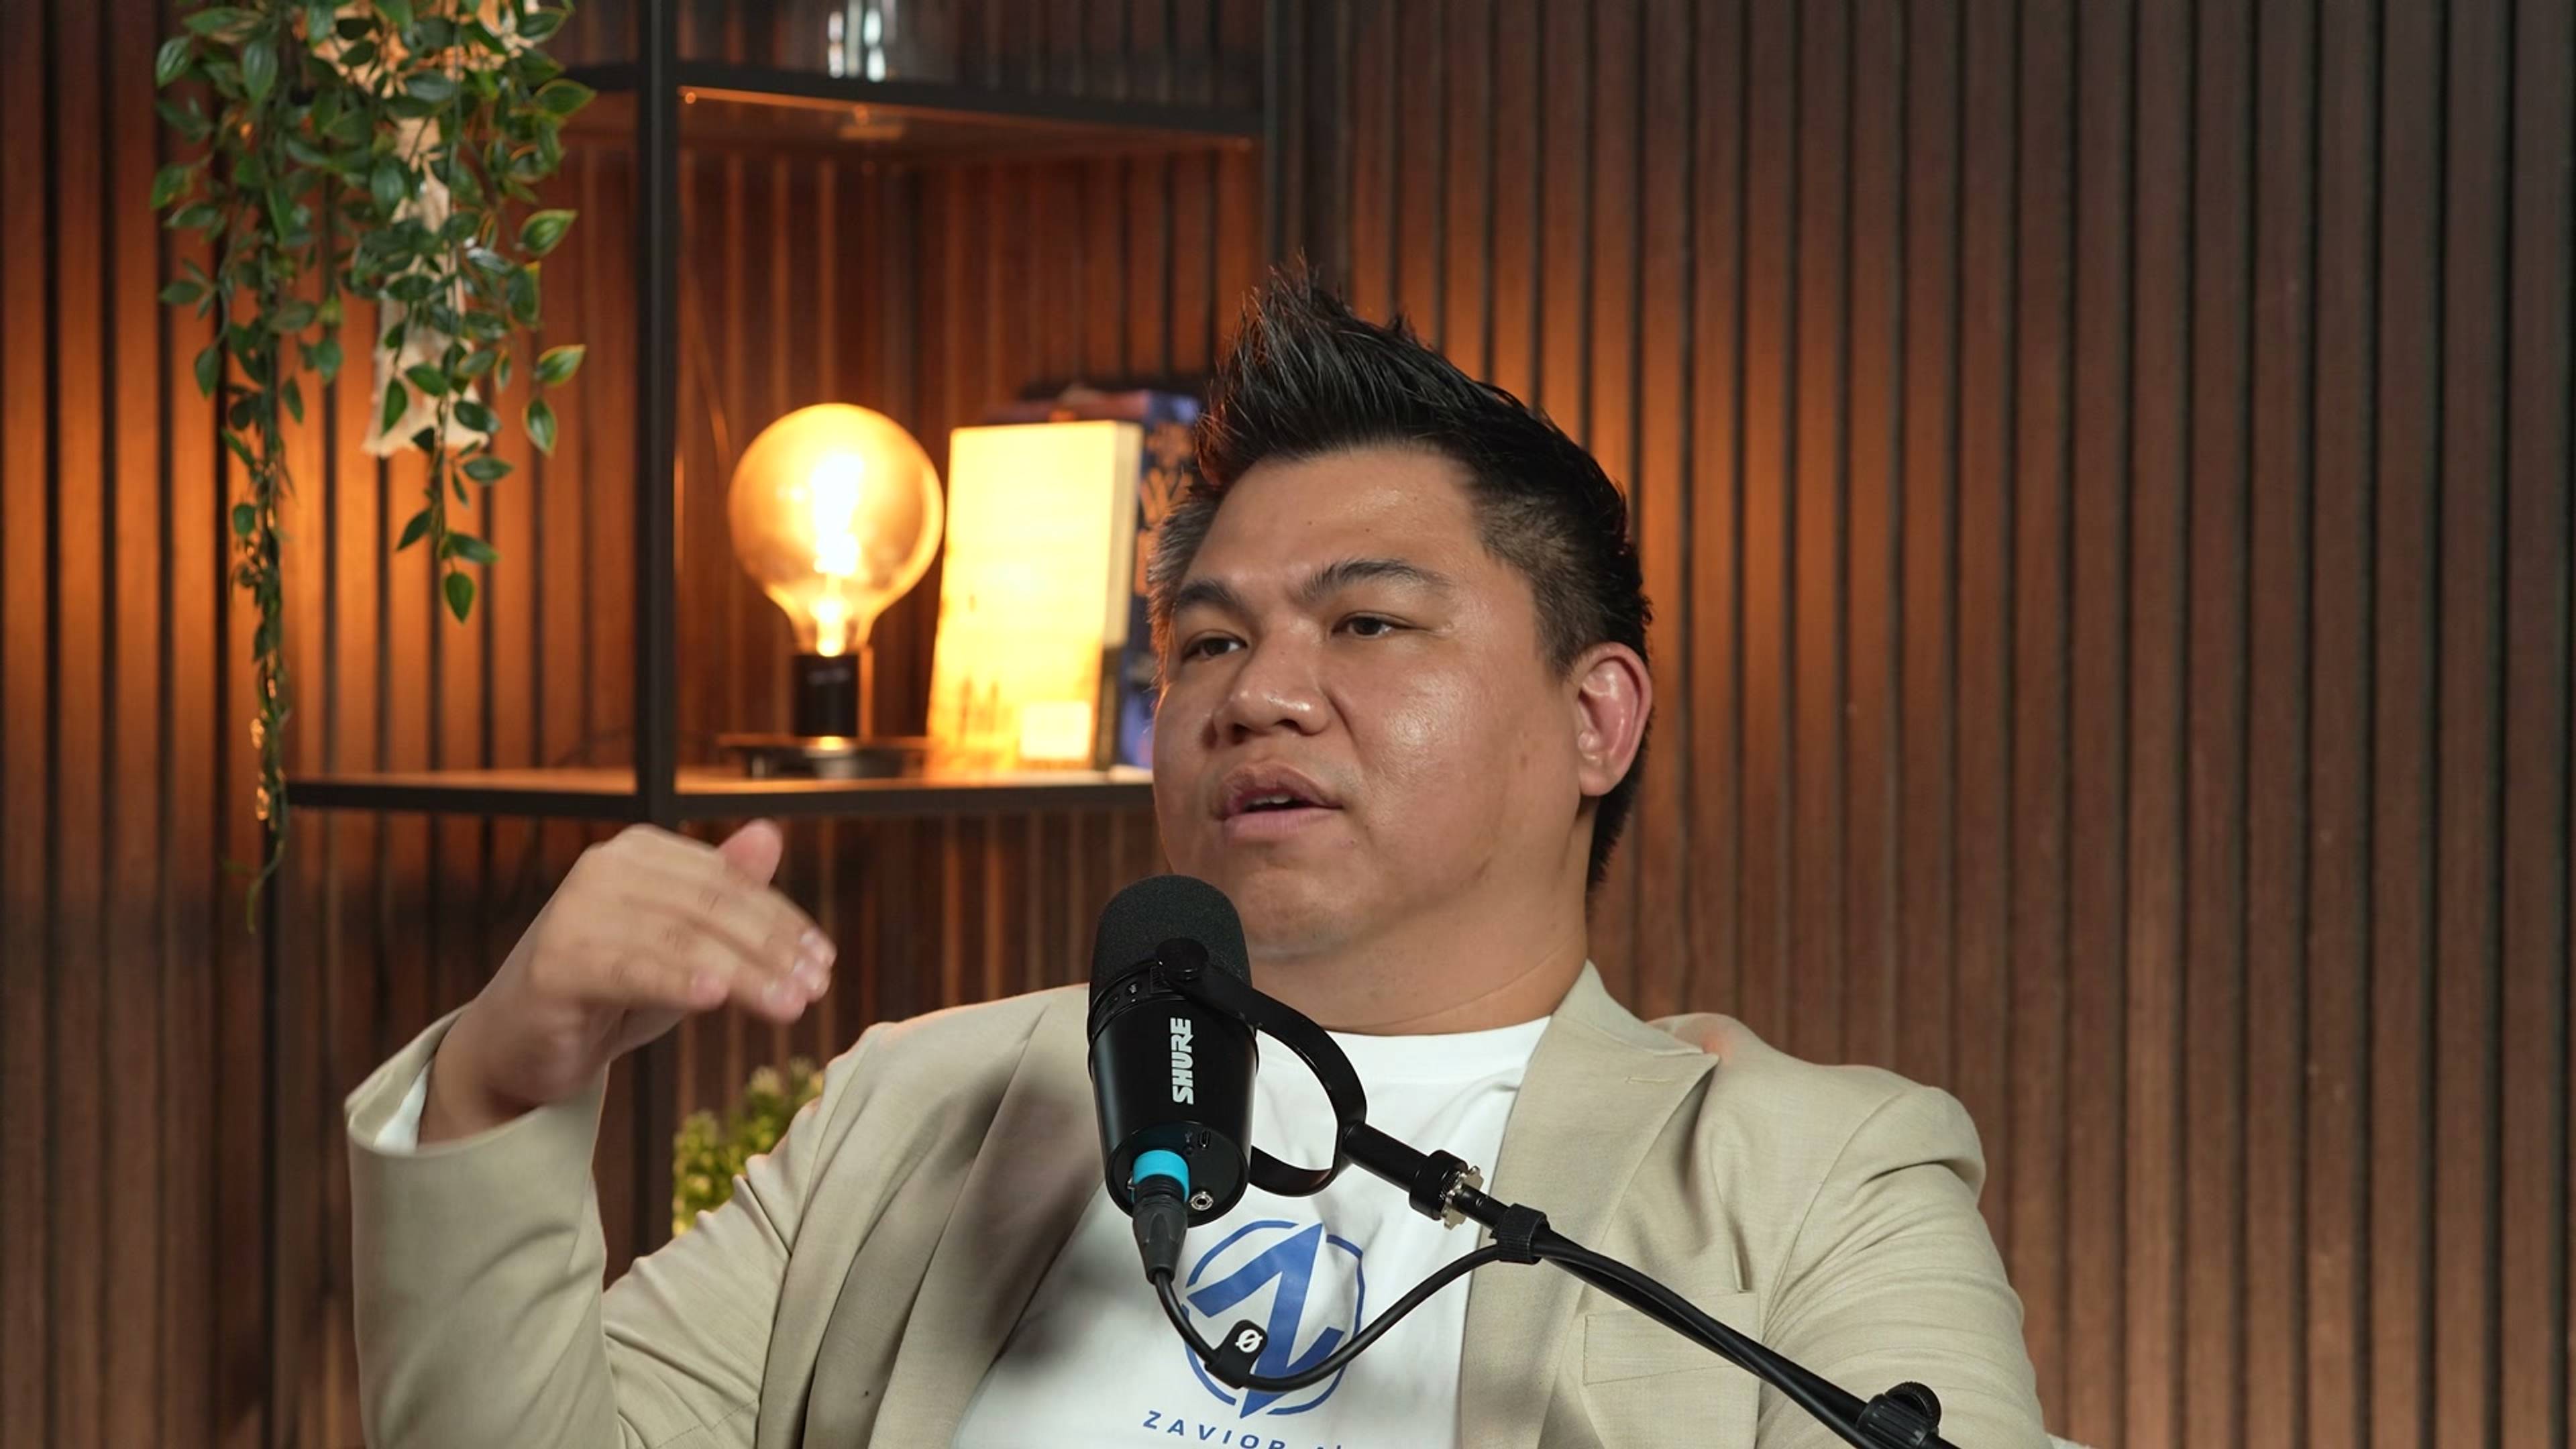
In our conversation, Glenn Tan, CEO and co-founder of Zavior, describes a hypothetical last-mile delivery business. Its valuable information could include how quickly drivers move between places and how many trips they complete in a period.
The sensitive detail may be the operating pattern: how quickly goods move and how much work the team completes. The person running that operation can explain why the pattern matters.
A list of names, passwords or payment-card numbers will not answer that question on its own. The operations owner may recognise a commercially useful combination that is hard to identify from individual field names.

Glenn TanCEO and co-founder of Zavior
Read the English transcript
Original interview extract: 52:20.80 to 53:09.76 in the original interview.
So beyond the standard guardrails that the existing modern LLMs have, we need to have business guardrails as well. What business guardrails means is that if I were to sell a service for last mile delivery, where is my main IP at? My main IP is actually possibly in the space of how fast my drivers move from one place to another and how many trips did they do in one time, right? In one phase or one term. So that information is now contextually my IP, right? In a way, if I want to put some guardrails, if I run a business like that, I will put guardrails around that kind of data not being shared.
Start with the employee's task
Take a fictional employee who wants help rewriting a customer update about a delivery delay. The source spreadsheet contains route IDs, exact driver timings, trip counts and internal margin notes.
For this exercise, the operations owner has approved a short service notice. The detailed operational file is not approved for this task. The employee can work from the notice without passing the spreadsheet to the assistant.
Fictional input-selection exercise
Task: Rewrite an approved customer notice in clear language.
Permitted input: Some deliveries may arrive one working day later than usual. We will send an updated delivery window.
Leave out:
- Route IDs and exact driver timings
- Trip counts and internal margin notes
- The original operational spreadsheet
Fictional example. The operations owner has approved this notice for this task only.
Ask the data owner to make the same distinction for one real recurring task: what does the employee need, and what does the source reveal that the task does not require?
Turn the decision into a check
Record the approved service, account, device and input path beside the permitted information. Security or IT can then check the configured policy on that exact route using synthetic content.
Compare a permitted notice with a separate fictional fixture containing the information the rule is meant to protect. Write down the expected response before testing, then record what actually happened. Check whether the remaining input still supports the employee's task.
If the expected control cannot be demonstrated, keep that question open and give it an owner. A successful check on one paste or upload path does not establish coverage for another.
Make the handoff clear
The business data owner decides which information is appropriate for the task. Security defines the required protection; IT verifies the supported configuration. The employee needs a short instruction and a place to ask about exceptions.
If an MSP or MSSP supports the rollout, identify the client's decision owner and the provider's technical support owner before the first pilot. A restriction should lead to a clear next step, not an unresolved handoff.
Provider training and retention terms are a separate part of the review. A no-training commitment does not decide which information the organisation permits the employee to send.
Define the next check
Use the sensitive-file scenario in Aona's policy-control guide to record the rule, test scope, expected response and next owner. Start with synthetic information.
Use the policy-control worksheet